Incident Command & Response
๐จ Emergency Incident Hotline
+1 (800) 555-9111 (Toll-Free 24/7)When ransomware strikes, manual reimaging cripples global enterprises. AEGIS instantly isolates infected systems, executes deterministic cryptographic state rollbacks, and restores total operational continuity without paying ransom or losing evidence.
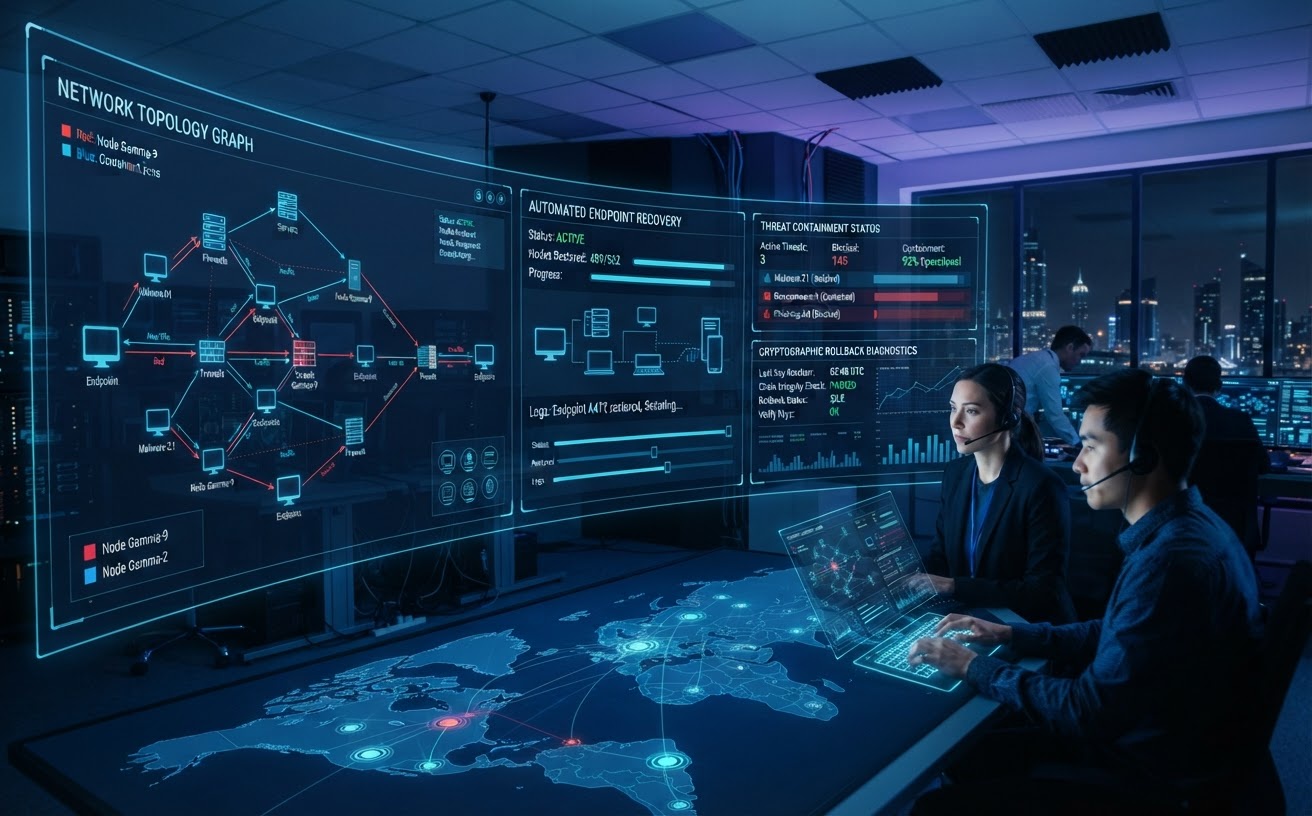
1,420 endpoints rolled back to Clean State Alpha (T-0:02s). Memory dumped to air-gapped forensic vault.
Audited benchmarks across Fortune 500 fleets recovering from high-impact ransomware and state-sponsored wiper attacks.
Cryptographic block rollback allows mission-critical hosts to resume normal operations in minutes, not industry-average 21 days.
Fully automated concurrent restoration across distributed hybrid fleets spanning 50,000+ endpoints simultaneously.
Immutable micro-snapshots ensure total file-level and database restoration without losing in-flight transactional data.
Eliminates downtime losses, forensic re-engineering fees, regulatory breach fines, and PR crisis management overhead.
Independent Benchmark Validation
Verified by Third-Party Cyber Risk Analysts across 1,200 simulated and live APT ransomware outbreaks.
Four synchronized pillars designed to neutralize systemic ransomware propagation, revive destroyed operating systems, and restore fleet health with zero operator friction.
Micro-delta differential protection captures cryptographically sealed point-in-time states every 60 seconds. Operates quietly below kernel level with zero perceptible impact on host CPU or end-user productivity.
When Master Boot Records (MBR), UEFI partitions, or disk partitions are corrupted or wiped by malicious payloads, trigger rapid zero-touch bare-metal provisioning over WAN, restoring verified golden images seamlessly.
Detect mass unauthorized file encryptions in memory. Instantly sever network sockets, freeze malicious execution trees, and revert file tables to the exact millisecond prior to the initial compromise.
Execute cryptographically signed remediation playbooks across 100,000+ endpoints simultaneously. Purge zero-day persistence artifacts, registry hooks, and compromised credentials within a single broadcast.
Native support for Windows Server & Workstations, macOS (Apple Silicon/Intel), RHEL, Ubuntu, Debian, SUSE, and virtualized VDI (Citrix/Horizon).
How AEGIS combines hardware-rooted identity, cryptographic snapshot rings, and cloud-to-edge distributed pipelines to guarantee uncompromised machine states.
Hierarchical snapshot hierarchy operates independently from the host operating system. Even if kernel integrity is wiped, offline hypervisor rings retain deterministic restoration hooks.
A recovered machine is never permitted to reconnect to enterprise networks without autonomous cryptographic inspection of firmware, secure boot status, and memory cleanliness.
Eliminates corporate network bottlenecks during fleet crises. Restorations employ encrypted P2P delta-mesh sharing, reducing uplink load from data centers by over 92%.
Step-by-step cryptographic sequence triggered upon anomalous execution or command authorization.
Physical NIC/Wi-Fi dropped from subnet; micro-hypervisor engages secure Out-of-Band management socket only.
Volatile memory dump and root-cause IOCs streamed to immutable cloud vault for legal/cyber-insurance compliance.
Encrypted/tainted sectors rewritten with pristine differential snapshots. Rebuilding master file tables instantly.
TPM 2.0 attestation passes; host identity certificates reissued; seamless user reconnect to production services.
A deterministic, forensics-grade containment and revival lifecycle that neutralizes adversarial persistence and reinstates complete workstation fidelity.
Cuts lateral propagation within 150 milliseconds of anomalous beaconing or bulk file modification. Silences all ingress/egress except for an encrypted, out-of-band C2 command pipe.
Captures cryptographic RAM state, registry hives, and volatile artifacts before sanitization. Tainted partitions are neutralized while preserving tamper-evident proofs for cyber insurers and law enforcement.
Deploys a hardened, fully patched operating system baseline from an uncompromised cloud repository. Overwrites compromised kernels, bootloaders, and firmware using out-of-band PXE or hypervisor rollback.
Re-injects the user's latest sanitized application states, encryption keys, and desktop configurations from pre-compromise micro-snapshots. Re-enrolls in corporate EDR/MDM with rotated tokens.
Every phase is signed with hardware-backed root keys. The resulting verifiable JSON/PDF ledger guarantees to board members, regulatory bodies (GDPR, HIPAA, SEC Cyber Disclosure), and insurers that no malicious residue exists on reinstated hosts.
Whether safeguarding air-gapped SCADA infrastructure, modern cloud VDI sessions, or remote executives on unmanaged Wi-Fi networks, AEGIS deploys uniformly.
Unified agent footprint across legacy servers, modern developer laptops, and mission-critical operating systems.
Instantaneous master template resetting for non-persistent and persistent cloud desktop infrastructures.
Deterministic recovery for headless point-of-sale systems, ruggedized healthcare terminals, and industrial controllers.
Maintains continuous zero-trust containment and restoration even when hosts are roaming behind hotel Wi-Fi or cellular tethering.
Bi-Directional API Hooks with Global EDR / SIEM / SOAR Leaders
Documented post-incident debriefs: How AEGIS defended critical infrastructure from nation-state ransomware and malicious supply-chain firmware corruptions.
A coordinated zero-day domain controller breach triggered BlackCat payload detonations across 42 acute care hospitals. Manual reimaging was estimated at 28 days with critical ICU surgeries facing cancellation.
A compromised third-party driver repository pushed a malicious signed UEFI payload rendering classified developer workstations unbootable (permanent black screen / boot-loop) across 12 countries.
โWhen ALPHV tore through our domain controllers on Thanksgiving Eve, AEGIS contained the spread automatically. Our hospital floor operations were back online before the extortion group even had time to send their ransom note.โ
Evaluate your current disaster recovery time objectives (RTO), forecast enterprise outage liability, and measure immediate financial risk reduction with AEGIS.
Adjust sliders to match your current enterprise footprint and recovery capabilities.
Simulations calibrated with NIST SP 800-34r1.